You are here:
Recognize Passkey Creation Prompt Behavior
Users see prompts to create a passkey in several situations, including after a sandbox refresh. The “Waive Multi-Factor Authentication for Exempt Users” permission applies only to customers with an active temporary extension for multi-factor authentication (MFA) enforcement.
Required Editions
| Available in: both Salesforce Classic and Lightning Experience |
| Available in: all editions |
When Users See “Create a Passkey” Prompts
With MFA enforcement, Salesforce requires employee users who don’t meet MFA requirements to register an MFA verification method. Salesforce defaults to a passkey-first MFA registration flow for all employee users. Salesforce requires users with privileged permissions to set up passkeys or another phishing-resistant MFA method. Users who don’t have privileged permissions still see the passkey prompt first, but they can choose to set up other MFA verification methods.
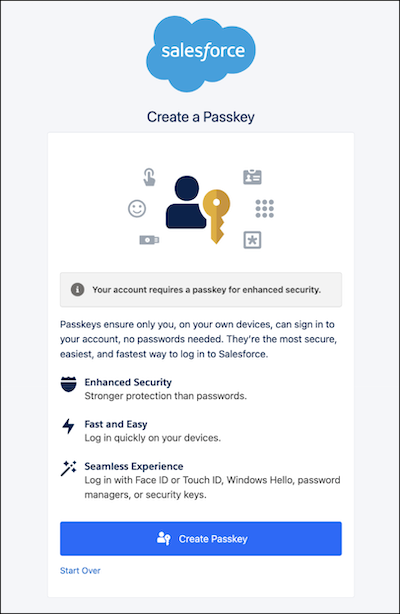
Users with privileged permissions see this prompt when they log in directly.
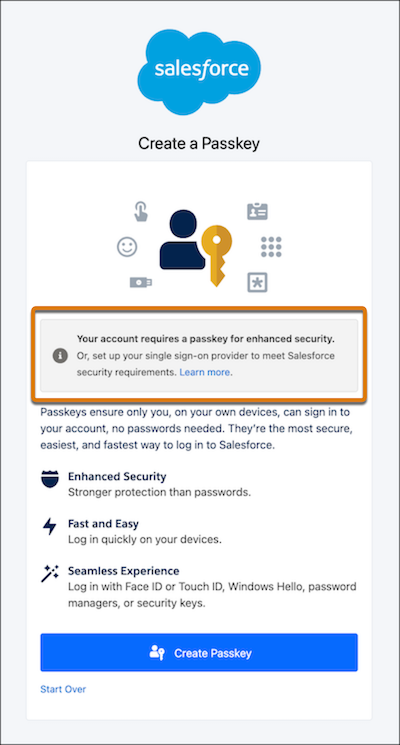
Users with privileged permissions see this prompt when they log in through a single sign-on (SSO) identity provider that doesn’t satisfy Salesforce MFA requirements.
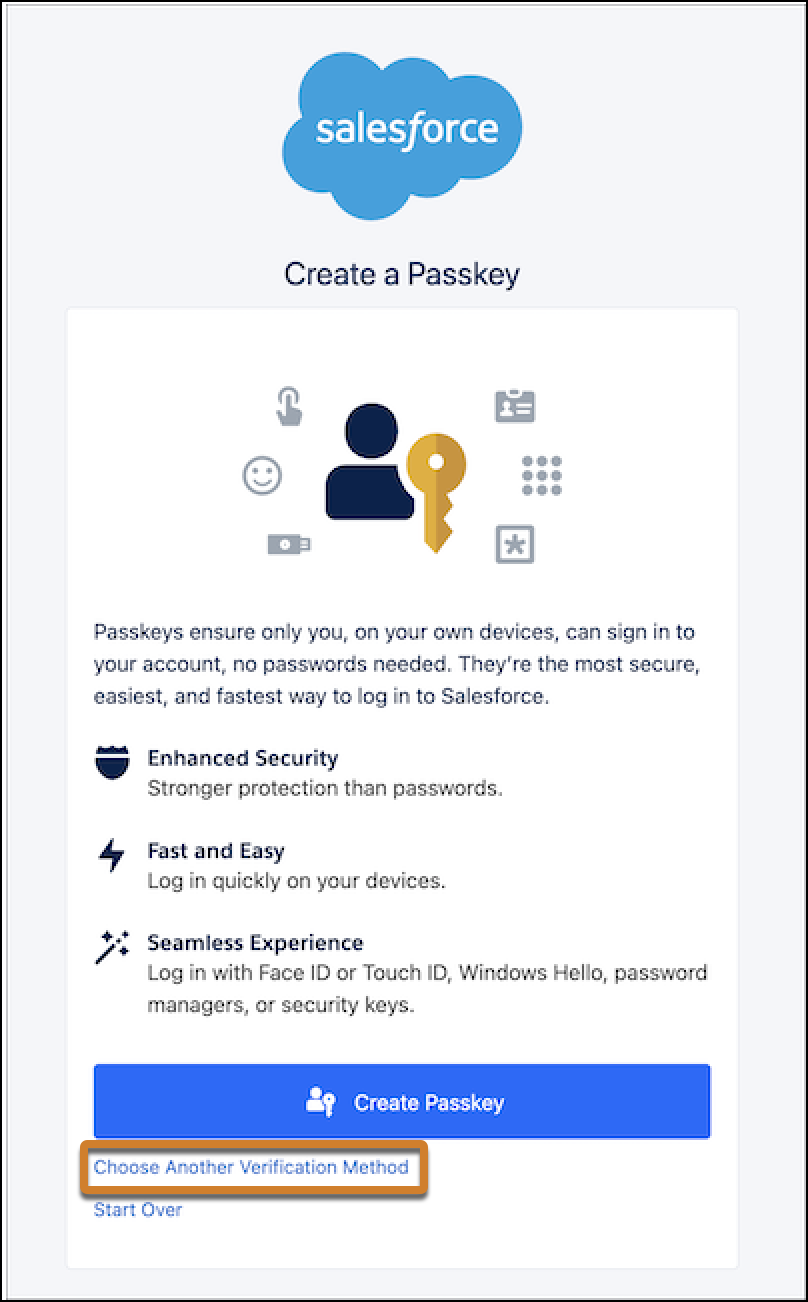
Users without privileged permissions see this prompt. They can click Choose Another Verification Method to set up Salesforce Authenticator or a third-party authenticator app instead. However, passkeys are still the first option shown to all users in the MFA registration flow.

The Choose Another Verification Method option isn’t available to users with privileged permissions.
Configure Passkeys After a Sandbox Refresh
After a sandbox refresh, users are prompted to create a passkey, even if they had one set up already. Newly refreshed sandboxes don’t inherit all verification settings from the production environment.
- Direct login and SSO: Users who had a passkey in production can see prompts to re-register in the refreshed sandbox until they complete the flow at least one time. Alternatively, they see a prompt to use their registered passkey, but the passkey doesn’t work.
- SSO only: Sandbox refreshes don’t fully inherit Security Assertion Markup Language (SAML) SSO configurations.
When users see these prompts, the required action varies based on the user’s login method.
-
Direct-login users: Follow the prompts at login to register a new passkey in the
sandbox.
If the sandbox prompts you to use your previously registered passkey and the passkey doesn’t work, get access to your account without a passkey. Then disconnect your current passkey and add a new passkey.
- SSO users: Create a passkey to log in, or get access to your account without a passkey. Then re-enable SAML in the refreshed sandbox. See SSO (Single Sign-On) SAML Settings Behavior During Sandbox Refresh — What Is Copied and What Changes.
Passkey Prompts for Users with the ‘Waive Multi-Factor Authentication for Exempt Users’ Permission
After MFA enforcement, users who previously had the ‘Waive Multi-Factor Authentication for Exempt Users’ permission see prompts to create a passkey. MFA enforcement causes this behavior. Unless your company has an approved temporary extension to use this user permission, this user permission no longer exempts users from MFA after enforcement.
For more information about MFA behavior with extensions, see MFA and Phishing-Resistant MFA Post-Enforcement Passkey Prompts and Extension Behavior.
